1 XMR = $558.94

Please login

Region:

Current view: Classic | Threads
Sort by: New | Tips

Bug Reports

Admin Admin Mediator Donor
N/A (0)
Posts: 54
Earned: 0.1 XMR
Tipped: 0 XMR
Reply to post #2089
Could you please describe the issue in more detail so our dev can look into it and fix it?
Edited: Sep 14 15:02
Tip Monero to Admin
QR Code 42DxmL7sdVzHU6fEocXioT1ZPf3n1CThA1HEbPVofKgC6GGG1oPYXXg6mbwMuZE4w3PkBF3UAWjhfMbMpu82dfmFJqGpsCb
Publish Tip to Admin

Please login to publish your tip
Juanperez7 Donor - Supporter
5 (2)
Posts: 7
Earned: 0 XMR
Tipped: 0 XMR
Reply to post #2090
1st: When trying to post with the city 'Miami', it won't go through; the platform will correct you saying 'Please check your listing details' and will only then provide you with a list of possible options saying 'Multiple cities found, please choose one'.
Suggesting cities as-you-type is more user friendly.

2nd: Even when typing a city outside the USA, the platform won't provide any options, and the pin will point at what it thinks is right (even pointing to a location >200 miles away from the desired location), leaving users stranded.
Tip Monero to Juanperez7

Juanperez7 has not setup a {COIN} tip address yet.

Publish Tip to Juanperez7

Juanperez7 has not setup a {COIN} tip address yet.
SoulReaver Donor - Resistor Mediator Top Seller
5 (4)
Posts: 105
Earned: 0.003 XMR
Tipped: 0 XMR
www.xmrbazaar.com serves a cert that does not cover it; HSTS includeSubDomains makes the failure unskippable

Summary
https://www.xmrbazaar.com presents a certificate whose names do not include the www host. The apex sends HSTS with includeSubDomains, so www is forced to HTTPS and fails closed with no proceed link. Links using the www host land users on a security warning instead of the site. Found via a link on a weblog (drukknoopje.nl) pointing at their profile. Their hosting provider reproduced it independently on their own machine and network: the apex URL loads for them, the same path on the www host fails, and they placed the fault on the www certificate.

Email from the mentioned weblog host:


Repro
Open https://www.xmrbazaar.com/
Chrome: NET::ERR_CERT_COMMON_NAME_INVALID, no proceed link (HSTS)
Brave: NET::ERR_CERT_COMMON_NAME_INVALID, no proceed link (HSTS)
Firefox: loads normally
The apex (https://xmrbazaar.com/) is unaffected in all three.

Expected
www serves the site under a cert naming www.xmrbazaar.com, or 301s to the apex over a valid cert.

HSTS state (chrome://net-internals/#hsts)
dynamic_sts_domain: xmrbazaar.com
dynamic_upgrade_mode: FORCE_HTTPS
dynamic_sts_include_subdomains: true
dynamic_sts_observed: 1788900429 (~2026-09-08)
dynamic_sts_expiry: 1820436429 (~2027-09-08)
static_sts_domain: (empty)

Expiry minus observed is 31536000, so max-age is one year. No preload entry, so the policy is header-set and fully under operator control. www holds no policy of its own and inherits the apex one.

What this establishes
www resolves and answers on 443: a handshake started and a cert came back.
That cert's name set omits www.xmrbazaar.com.
includeSubDomains asserts every subdomain speaks valid HTTPS. www does not. Each setting is fine alone; together they produce a hard failure with no click-through.
The policy is re-observed on every apex visit, so the one-year max-age does not lapse for regular users. This will not self-heal.

Scope
Client side only. I have not seen the server config, so I am not asserting whether the cert omits the www SAN or whether www terminates on a different host or edge. The Firefox result is an observation; I did not establish why it differs.

Checks
openssl s_client -connect www.xmrbazaar.com:443 -servername www.xmrbazaar.com /dev/null | openssl x509 -noout -subject -ext subjectAltName
dig +short www.xmrbazaar.com
curl -sSI https://xmrbazaar.com | grep -i strict-transport-security

Potential Fix
Reissue the certificate so it carries both the apex and the www host, and add a server-level 301 from www to the apex so the canonical URL is unchanged. On Let's Encrypt that is a second -d flag on the existing certbot command.

Two things that do not work: removing the www DNS record leaves every browser holding the cached policy still forcing HTTPS on www, and dropping includeSubDomains takes up to a year to age out. Issuing the cert for both names is the only fast path.

Impact
Third-party links using the www host, including the one on the weblog, show users an unskippable warning about attackers intercepting passwords and messages.
Leaving users confused.
Edited: Sep 15 16:49
Tip Monero to SoulReaver
QR Code 8AJJt5FoxgKapYk69YgSLXPaSBYd88hghg32ie25ZXGSFFYgVeKT4ytLkPoCsnJGE3gQninbK6JDUAX4qNCRUqfXFwXe3Hm
Publish Tip to SoulReaver

Please login to publish your tip

Juanperez7 Donor - Supporter
5 (2)
Posts: 7
Earned: 0 XMR
Tipped: 0 XMR
Reply to post #2090
Hi guys, do you have any updates regarding this issue?
Thank you.
Tip Monero to Juanperez7

Juanperez7 has not setup a {COIN} tip address yet.

Publish Tip to Juanperez7

Juanperez7 has not setup a {COIN} tip address yet.
UsualCat
5 (7)
Posts: 6
Earned: 0 XMR
Tipped: 0 XMR
Simplex Notification seems not sent as realtime as they arrived. i had 2 new chat but i didn't hear anything from simplex notification

last week it come the day after the actual chat arrived
Tip Monero to UsualCat

UsualCat has not setup a {COIN} tip address yet.

Publish Tip to UsualCat

UsualCat has not setup a {COIN} tip address yet.

UsualCat
5 (7)
Posts: 6
Earned: 0 XMR
Tipped: 0 XMR
Reply to post #2115
after doing some check
by unbind and re-bind it
they (simplex) seems still error
with " API error"
Tip Monero to UsualCat

UsualCat has not setup a {COIN} tip address yet.

Publish Tip to UsualCat

UsualCat has not setup a {COIN} tip address yet.

stonego
5 (1)
Posts: 1
Earned: 0 XMR
Tipped: 0 XMR
I tried to create a sale, but when I send it, it changes to an auction
Tip Monero to stonego

stonego has not setup a {COIN} tip address yet.
Publish Tip to stonego

stonego has not setup a {COIN} tip address yet.
WiseGuy92
5 (2)
Posts: 2
Earned: 0 XMR
Tipped: 0 XMR
Update to my previous post: QR code scanning on GOS fails on dark mode of the site but works on light mode, desktop.
Tip Monero to WiseGuy92

WiseGuy92 has not setup a {COIN} tip address yet.

Publish Tip to WiseGuy92

WiseGuy92 has not setup a {COIN} tip address yet.

SoulReaver Donor - Resistor Mediator Top Seller
5 (4)
Posts: 105
Earned: 0.003 XMR
Tipped: 0 XMR
Follow-up bug report: og:url still hardcoded on listing pages, and robots.txt points to another site's sitemap

Checked 2026-09-21. Two independent issues, both reproducible with curl (commands at the end).

1. og:url is hardcoded to the homepage on every listing (follow-up to my earlier report)
Severity: medium. Breaks link previews for every listing on platforms that key cards on og:url.

Observed: listing pages emit the same og:url as the homepage, logged in and logged out. Example, /listing/7imv/:
[code][/code]
The listing's og:title, og:description, og:image and twitter:* tags are all listing-specific and correct. og:url is the only one that isn't.

Impact: platforms that use og:url as the canonical key for preview cards treat every listing as the same page. On Mastodon (reproduced in my earlier report), all listings resolve to one shared card record, so a shared listing can show another listing's card, and older posts on the same instance can change when a newer listing gets fetched.

Not affected: X/Twitter keys cards on the posted URL, so this bug doesn't touch it. A card there that was missing its image was fixed by forcing X to re-crawl, with no site change, so that one is X-side caching.

Fix: emit the listing's own URL, in the same trailing-slash form the site links to:
[code][/code]
The homepage value is correct as is.

Optional: listing images are already re-encoded server-side (GD, 1200 px wide; the /listing/JJsd/ image is 1200x1600, 575 KB), so the dimensions are known at upload. Emitting og:image:width and og:image:height lets Facebook render the image on first share, per its sharing docs.

2. robots.txt advertises a sitemap on bitejo.com, a domain now parked and listed for sale
Severity: low. SEO only, one-line fix.

Observed:
[list]
[*]https://xmrbazaar.com/robots.txt
[code]User-agent: *
Allow: /

Sitemap: https://bitejo.com/sitemap.xml[/code]
[*]That sitemap contains a single URL, https://bitejo.com/lander, and no xmrbazaar.com URLs.
[*]https://xmrbazaar.com/sitemap.xml returns 404.
[*]In a browser, bitejo.com redirects to a GoDaddy aftermarket "for sale" page (buy-now price $299 as of 2026-09-21). WHOIS shows it was created 2026-07-18 (Namecheap), so any earlier registration lapsed and the name was registered fresh and listed for sale.
[/list]

Likely cause: a leftover from reused code rather than an intentional setting.

Scope: I found no other references to bitejo.com in the homepage, a listing page, /js/trollbox/init.js, /js/pwa/init.js or /manifest.json, so nothing on the site loads from it.

Impact: crawlers are pointed at a sitemap that lists none of XmrBazaar's pages, so the site effectively has no sitemap. And because XmrBazaar's own robots.txt references that file, whoever buys bitejo.com controls the sitemap XmrBazaar advertises to search engines.

Fix: remove the Sitemap line or replace it with an xmrbazaar.com sitemap.

Reproduce
[code]# 1. og:url on a listing
curl -s https://xmrbazaar.com/listing/7imv/ | grep -o ']*>'

# 2. sitemap
curl -s https://xmrbazaar.com/robots.txt
curl -s https://bitejo.com/sitemap.xml | grep -oE '[^
Edited: Sep 22 03:33
Tip Monero to SoulReaver
QR Code 8AJJt5FoxgKapYk69YgSLXPaSBYd88hghg32ie25ZXGSFFYgVeKT4ytLkPoCsnJGE3gQninbK6JDUAX4qNCRUqfXFwXe3Hm
Publish Tip to SoulReaver

Please login to publish your tip
42069 Donor - Supporter
N/A (0)
Posts: 1
Earned: 0 XMR
Tipped: 0 XMR
Pagination for the wishlist doesn't work. adding ` ?per_page=250 ` to the end of one's wishlist merely allows one to see more results.

Not shure if there is a bug bounty but if so ping me.
Tip Monero to 42069
QR Code 864bSsnpgq9guUzu54XvftLnX4EaDqHJ1hH8TqGVmB3jdK8KLSAgvA4AH2in11SpbYZravVpTr7C9AQATTaSuwYu1A26WDV
Publish Tip to 42069

Please login to publish your tip
NataL1na24
5 (1)
Posts: 1
Earned: 0 XMR
Tipped: 0 XMR
I think i accidentally refreshed the order page and now it says under Escrow "Error: Invite was already used", is there a way to fix this?
Tip Monero to NataL1na24

NataL1na24 has not setup a {COIN} tip address yet.

Publish Tip to NataL1na24

NataL1na24 has not setup a {COIN} tip address yet.
SoulReaver Donor - Resistor Mediator Top Seller
5 (4)
Posts: 105
Earned: 0.003 XMR
Tipped: 0 XMR
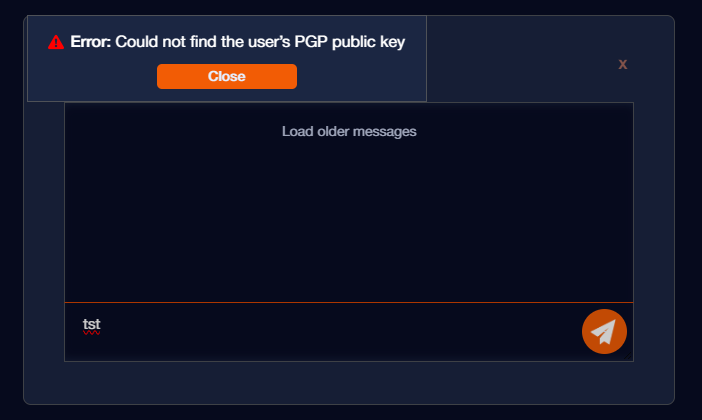
Bug Report: Missing PGP Key on User Profile

Target URL: https://xmrbazaar.com/messenger/schnur/
Affected Account: schnur

Description:
The messenger interface for user schnur does not display an associated public PGP key. End-to-end encrypted messaging and cryptographic identity verification cannot be established for this trade/chat session.

Steps to Reproduce:

Open active messenger session at https://xmrbazaar.com/messenger/schnur/.


Inspect the user details / key section.

Observe that no public PGP key is present or bound to the account.

Expected Behavior:
The user's public PGP key should be rendered on the messenger view, or the platform should enforce public key association for active trading/messaging profiles.
Tip Monero to SoulReaver
QR Code 8AJJt5FoxgKapYk69YgSLXPaSBYd88hghg32ie25ZXGSFFYgVeKT4ytLkPoCsnJGE3gQninbK6JDUAX4qNCRUqfXFwXe3Hm
Publish Tip to SoulReaver

Please login to publish your tip
glamorous_oak Donor - Supporter Top Seller
5 (76)
Posts: 33
Earned: 0 XMR
Tipped: 0 XMR
Reply to post #2150
yes can confirm i am unable to complete an order because of this. We talked in the past but now i can only receiver schnur's messages not respond.

i asked AilliA and the response is:
"It appears to be a v5 key which OpenPGP.js devs found controversial for some reason. Although there is a config option “enableParsingV5Entities“ which we can enable."

I hope this gets fixed soon or schnur happens to find this here.
Edited: Sep 25 22:00
Tip Monero to glamorous_oak
QR Code 852XVfJZLuXC5FGqTNXdKB7c8AwLgWgTfH8Kr2P48VAAKbGSXyBXV2qDYwyHScfGhTRLaM1C3CdzogtgUAeZVxQC7hw4KHy
Publish Tip to glamorous_oak

Please login to publish your tip
NoReply
N/A (0)
Posts: 3
Earned: 0 XMR
Tipped: 0 XMR
[b]Manual PGP messages can be delivered encrypted to the wrong key[/b]

Not sure if this counts as a bug or just a gap, but it seemed worth raising.

[b]What happened[/b]

A message from mutterficker arrived that my client could not decrypt. The account uses the No-JS manual PGP messenger (its published key is self-generated rather than a JS messenger key). The message carries a single recipient key ID, ca87592dd66e742a, which is mutterficker's own encryption subkey. My key is not among the recipients, so it can never be decrypted on my side.

In the JS messenger the client encrypts to both the recipient and the sender automatically, so this cannot happen there. In manual mode the sender encrypts with their own tools, and as far as I can tell nothing checks the result, so the platform delivered it as if it had worked. Presumably the sender believes it went through.

[b]Suggestion: check recipients on manual messages[/b]

The recipient key IDs in a PGP message are readable without decrypting anything. They sit in the clear in the packet headers, ahead of the encrypted data. So the server could check whether a manually encrypted message includes the recipient's key before accepting it, and warn the sender if it does not. Nothing is decrypted, so it stays end to end.

If you add this, treat an all-zero key ID as unknown rather than wrong, since gpg --throw-keyids hides recipients that way on purpose.

[b]Small related thing: the error message[/b]

The interface showed: "Decryption key not found. If you reset your recovery code recently, please ask the sender to send you this message again."

My recovery code had not been reset. The message just was not encrypted to me. The suggested cause points a user toward resetting their key, which as I understand it would permanently lose access to their existing messages. Something like "This message could not be decrypted with your key. It may have been encrypted to a different key, or your recovery code may have changed" would cover both cases, including senders on the manual messenger, without nudging anyone toward a destructive fix.

[b]Also: make the manual messenger easier to find[/b]

The FAQ says manual PGP is available for users who do not want JavaScript, at https://xmrbazaar.com/messenger-nojs/, but the only place I found a link to it was the FAQ. I did not know the mode existed until I went looking, which is part of why this message confused me in the first place. Listing it under settings, next to the JS messenger, would let people who want it actually find it, and would make it more obvious to everyone else that a message can come from a sender encrypting manually.
Edited: Sep 25 22:17
Tip Monero to NoReply

NoReply has not setup a {COIN} tip address yet.

Publish Tip to NoReply

NoReply has not setup a {COIN} tip address yet.
schnur
5 (2)
Posts: 4
Earned: 0 XMR
Tipped: 0 XMR
Reply to post #2154
-----BEGIN PGP SIGNED MESSAGE-----
Hash: SHA512

Hey guyyyss,
the issue was that I was changed my pubkey to some post quantum algorithm, ed448 to be exact.
See my suggestion promoting pq here: http://XmrBazaar6wzcr3wvj4anpnfwv5tcikgdurtzzfba233g52fa2fjx3qd.onion/forum/topic/252/

The problem is that gpg2.5+ supports it, but not gpg2.4, which is distributed my most linux distros. I just forgot that other users could have issues with it, you're probably helpless to if you don't know about different crypto algorithms.

Solutions right now:
Don't be like me and upload pq keys lol
Install GnuPG 2.5. I don't know how Sequoia handles post quantum algos. (No-JS!)
-----BEGIN PGP SIGNATURE-----

iJEEARYKADkWIQTmfT6IO4V5ubJXjE2918CSol9kIAUCardDyhsUgAAAAAAEAA5t
YW51MiwyLjUrMS4xMiwyLDIACgkQvdfAkqJfZCAFuAD+LWzbPgKqHK0ZIDeYfkEW
bSCQubqwY243mfArh1zYyQ8BAKTZ2GJ1L0P72LOIlBAArmX3Qmbue3sPkzaHtr45
AMEIiMUFARYKAEUiIQVLHEGnS9Bn6+dQzzXz7O3lyERqNwgKikUnhvlS+PVShAUC
ardDyhsUgAAAAAAEAA5tYW51MiwyLjUrMS4xMiwyLDIAAD2UAciZ81ZRqGkkyRr9
9B/0PjyzDvvQ3DPC+NBKhVc28BxF+9ZIKW+YSJEKK8QjjQ0q/EpzmW34Et36aIAB
yNuNITKWJmdhsd9mQdzgcM4+PU9TKIMuUgS+r51KT83PjiLW1CvaclJqEq244Wle
/xrsQzjhp+ccAA==
=nXOB
-----END PGP SIGNATURE-----
Tip Monero to schnur

schnur has not setup a {COIN} tip address yet.

Publish Tip to schnur

schnur has not setup a {COIN} tip address yet.

You must login in order to publish a post